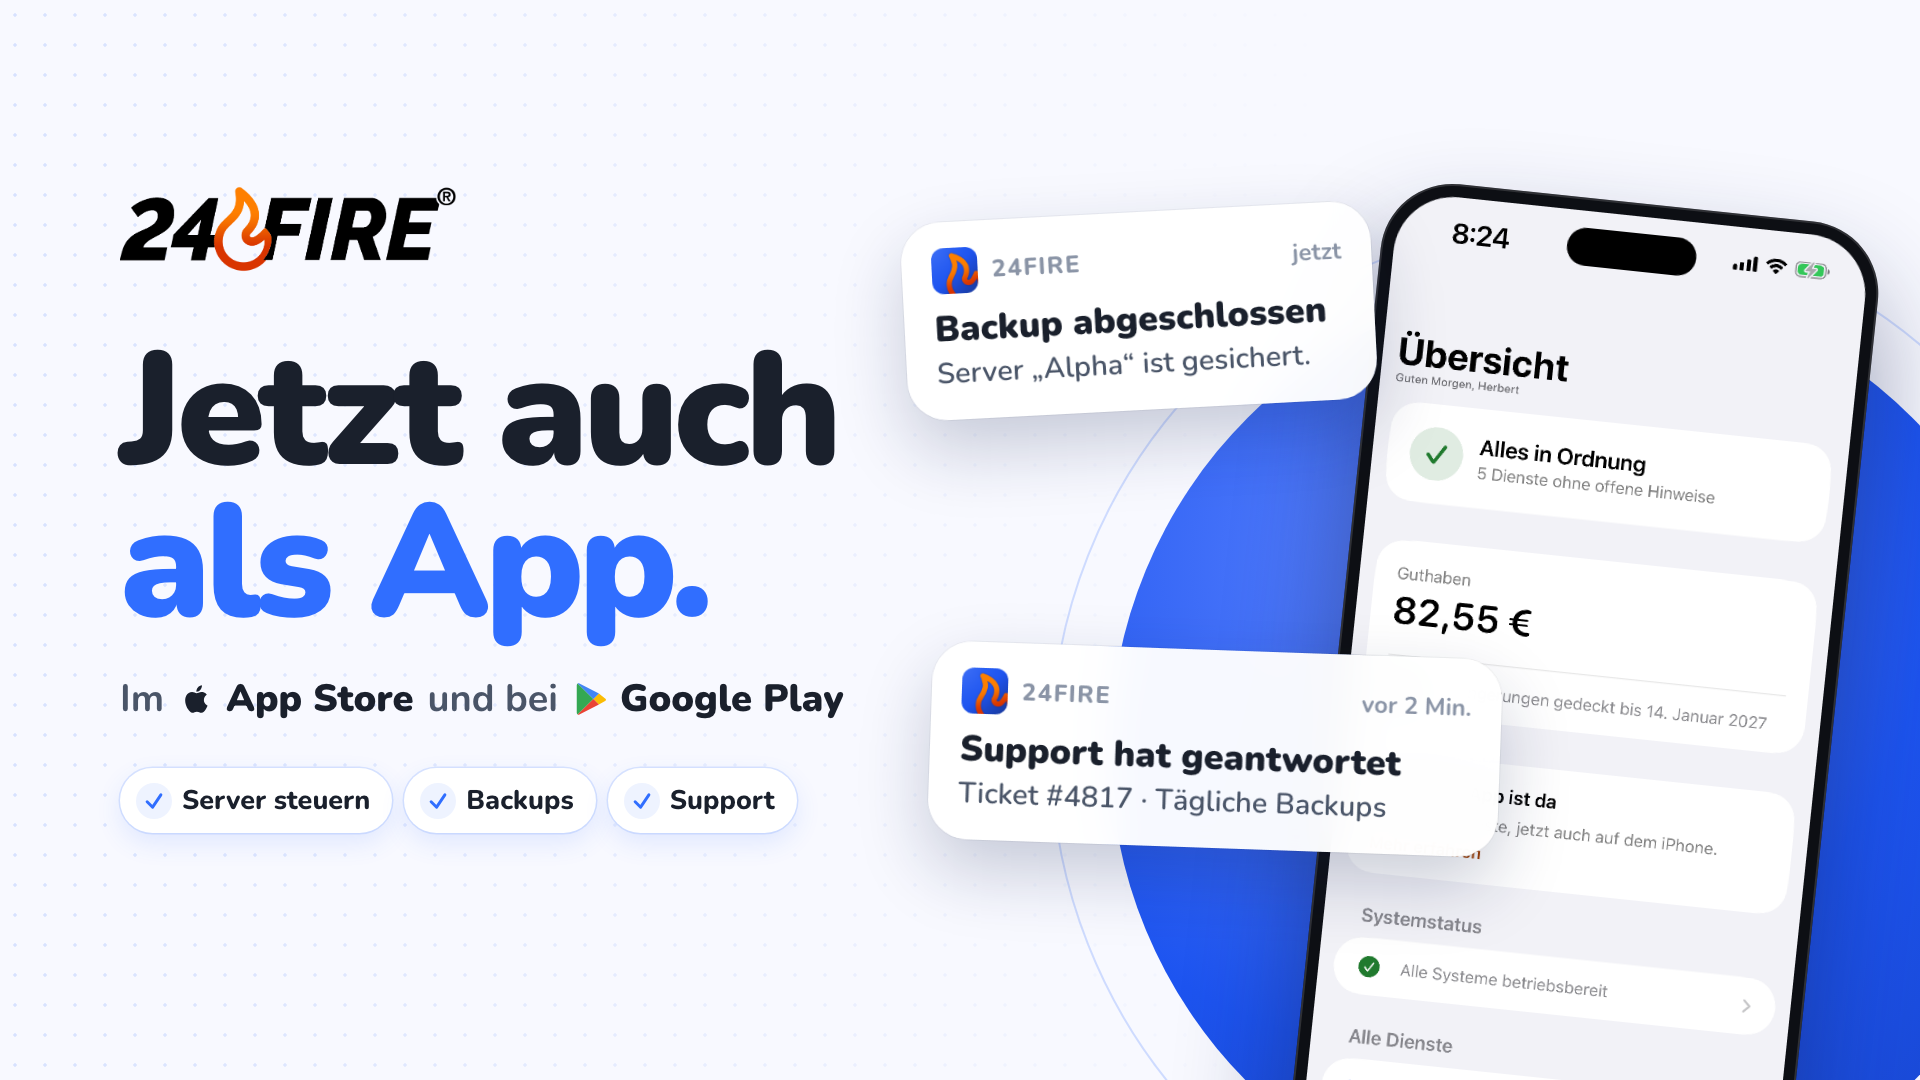





FireID Connect adds another way to sign in to the Control Panel. The sign-in page shows a QR code, you scan it with the 24fire app and confirm the sign-in on your smartphone. You do not enter an e-mail address, password or two-factor code.
You need the 24fire app for iPhone or Android on a device that is paired with your account. The existing sign-in methods with password, two-factor code and passkeys remain unchanged.
Anyone signing in without a password is right to ask how secure that is. You manage servers, domains and credit through the Control Panel, and our standards for every sign-in method are correspondingly high. FireID Connect offers a considerably higher level of protection than signing in with a password and two-factor code, because no secret is transmitted that could be intercepted, guessed or reused elsewhere. So that you can judge this for yourself, this post first gives brief instructions and then explains how a sign-in works technically, which cryptographic methods it relies on and how it is protected against attacks.
Signing in, in three steps
- On the sign-in page, choose “Sign in with FireID Connect”. The browser shows a QR code that is valid for around two minutes and is then renewed automatically.
- In the 24fire app, tap the QR icon on the overview and scan the code. Your smartphone’s camera recognises the code as well and takes you to the app.
- The app shows which browser wants to sign in, with IP address, country and time. You confirm with Face ID, fingerprint or your screen lock. The browser is then signed in.
Nothing more is needed to sign in. The following sections describe what happens in the background and why third parties cannot exploit this process.
Technical process
A sign-in consists of four operations between your browser, the 24fire app and our systems.
Creating the request. When you open FireID Connect, our systems generate two independent random values from a cryptographically secure random number generator. The first is displayed in the QR code. The second is bound to the session of the browser showing the code. It is neither part of the QR code nor visible to the app. The QR code contains no account information.
Redeeming the code. The app sends the scanned value to 24fire over its authenticated connection. Each code is accepted there only once. Our systems then create an approval request that is bound to the scanning device and generate a challenge for it. This is a further random value that is valid for this one request only.
Signing the approval. The app displays the details of the sign-in. After you confirm, the smartphone creates a digital signature. It covers the identifier of the request, the challenge, the purpose “sign-in”, a hash of the displayed details and your decision. A decline is signed in the same way.
Verifying and collecting. We verify the signature with your device’s public key. If it is valid, the browser can collect the sign-in. Only the session to which the second random value from the first step is bound can do so, and only once. Before the browser session is created, the account goes through the same checks as with any other sign-in.
Cryptographic basis
FireID Connect is based on asymmetric cryptography with elliptic curves. Passkeys under the FIDO2 standard and SSH keys use the same class of methods.
One key pair per device. When you pair your smartphone, it generates a key pair. The private key is held in the device’s hardware-backed key store, cannot be read out and is only released for a signature after Face ID, fingerprint or screen lock. Only the public key is sent to 24fire. It can be used to verify signatures, but not to create them. During pairing, we already check that the submitted key matches the intended method and reject all others.
Challenge-response. With a password, the secret itself is transmitted. With FireID Connect, our systems send a random value to the app and the smartphone proves with its signature that it holds the private key. The key itself is never transmitted. Anyone reading the connection obtains nothing that could be used for another sign-in.
A signature over the specific request. The signature is valid for exactly one request with exactly the details the app displayed. Two checks ensure this. The app calculates the hash of the displayed details itself and does not show the request if it differs from the value we sent to it. On our side, the message to be verified is assembled from the values we have stored. Nothing is taken from the app’s response for this.
Single-use values. The challenge is consumed with the decision. Both happen in a single step, so there is no gap between the decision and the challenge being consumed. A second decision on the same request is therefore ruled out.
Stored as hashes. The value from the QR code and the value of the browser session are held in our database only as one-way hashes.
The security of the process therefore depends on the private key in the smartphone, not on the process remaining secret. That is why we can describe it here. The only things we do not publish are operating parameters such as the thresholds of our abuse detection.
Protection against attacks and tampering
Photographed or forwarded QR code. The value in the QR code is not enough to obtain a session. Only the browser that created the code can collect the sign-in. Someone who photographs your code does not get into your account with it.
Fake sign-in page. The most important attack on any QR code sign-in is known as QRLjacking. An attacker creates a code in their own browser and shows it to you on a fake page so that you scan and confirm it. Three measures work against this. Before you confirm, the app shows the browser, IP address and country of the requesting session, in this case the attacker’s details, and this information is part of the signature. After the scan, the genuine browser shows the details under which it appears in the app, so you can compare both displays. In addition, a code is valid for only around two minutes for scan and confirmation together. The decision still rests with you: if the details in the app do not match your browser, decline the request. Only scan codes on cp.24fire.de and do not pass them on.
Replaying an approval. Every signature contains the challenge of its request. As the challenge is consumed with the decision, a recorded signature does not match any later request. Redeeming the code and collecting the sign-in in the browser are each possible only once as well.
Guessing codes. The random values are long enough that a valid code cannot be found by trial and error within its validity period. In addition, the number of codes that can be created and redeemed within a period is limited. Our systems respond identically to unknown, expired and already redeemed codes, so the responses do not reveal whether a code exists.
Altered sign-in details. If the details are altered on their way to the app, the hash calculated by the app no longer matches the value we sent and the app does not show the request. We reject a signature over any data other than the data we have stored.
Approval from another device. Only the device that scanned the code can decide. What counts is the key used for signing. A copied session token of the app is therefore not sufficient, as the private key does not leave the smartphone.
Access to the database. Our database holds hashes of the codes and public keys. Neither can be used to create a valid code or a valid signature.
Two-factor authentication
FireID Connect does not ask for a two-factor code, even if you have enabled two-factor authentication. The approval already contains two factors: possession of the paired smartphone with its private key, and Face ID, fingerprint or screen lock on the device. A six-digit code is a value that can be intercepted and entered elsewhere. A signature is bound to a single request and worthless outside it.
The other checks on your account apply unchanged. A deactivated or temporarily protected account cannot be signed in via FireID Connect either.
If you lose your smartphone
Every approval requires Face ID, fingerprint or the screen lock. A locked smartphone in someone else’s hands therefore cannot be used to sign in. You can also remove the pairing in your account’s security settings. We will then no longer accept signatures from that device. Your password, two-factor settings and passkeys are not affected, so you can continue to sign in as usual.
Setup
- Get the 24fire app for iPhone or Android and pair your device. The introduction of the app shows how.
- The next time you sign in to the Control Panel, choose “Sign in with FireID Connect”.
Our support team takes questions and feedback via ticket.